Who Actually Executes the Action? Security Across AI Integrations
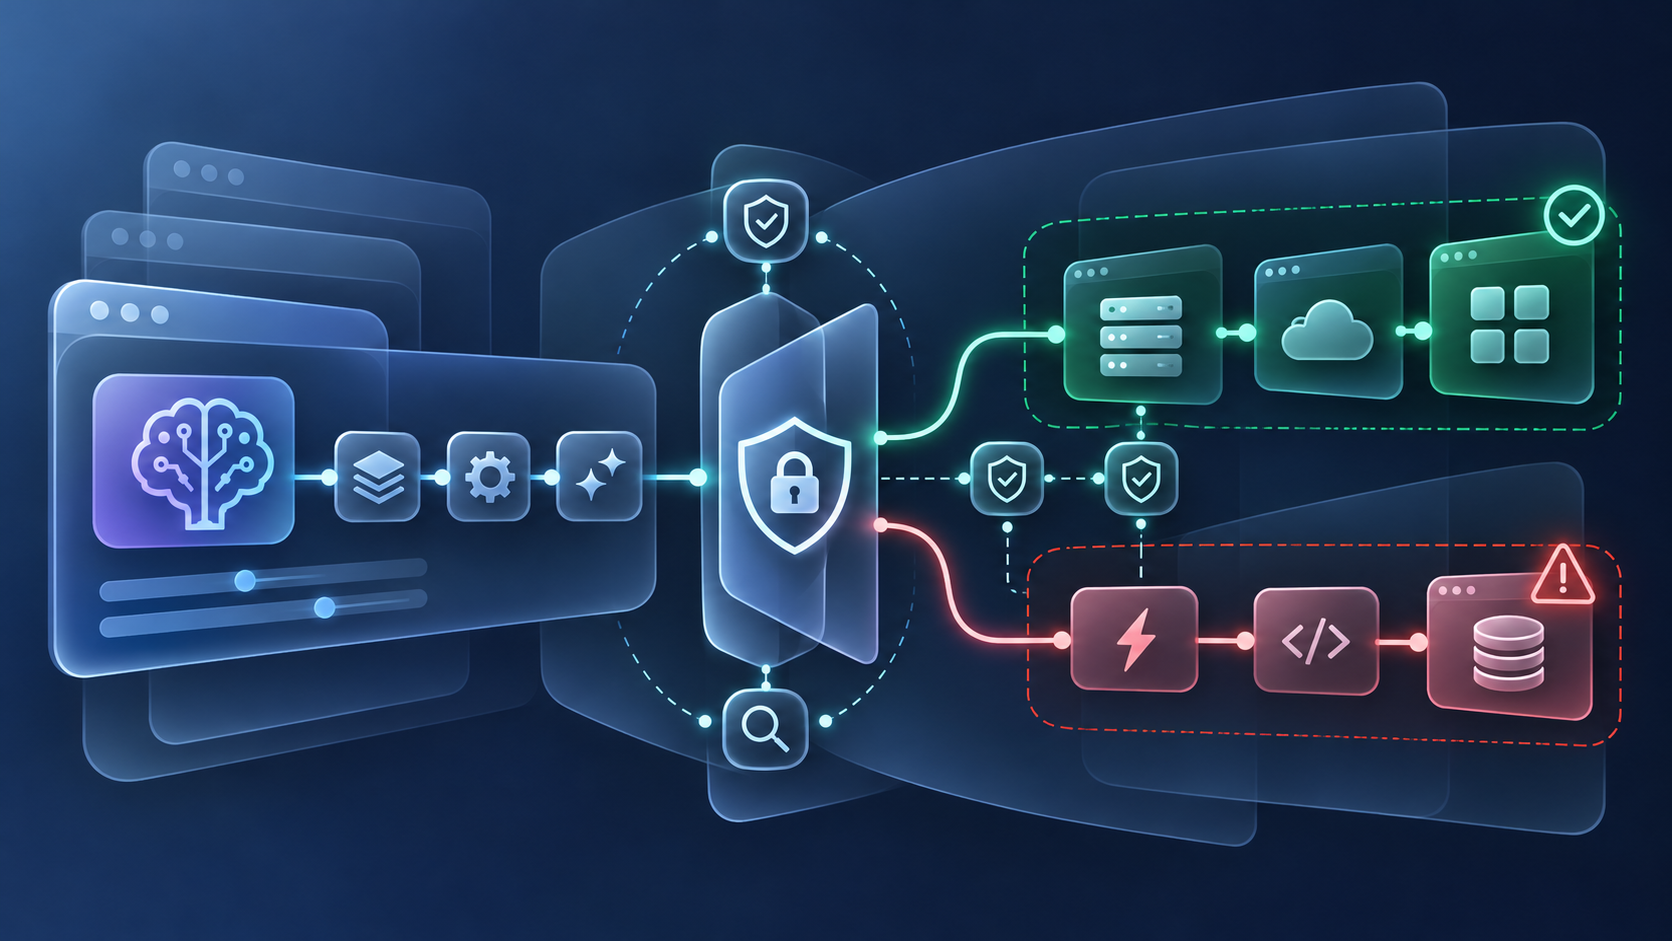
AI-powered workflows can cross application boundaries and execute operations beyond their intended scope. How should engineers enforce security across connected systems?
I develop AI agents, automated workflows, and user-focused software with Python and TypeScript.
"Failure is an opportunity to learn and thrive."

AI-powered workflows can cross application boundaries and execute operations beyond their intended scope. How should engineers enforce security across connected systems?

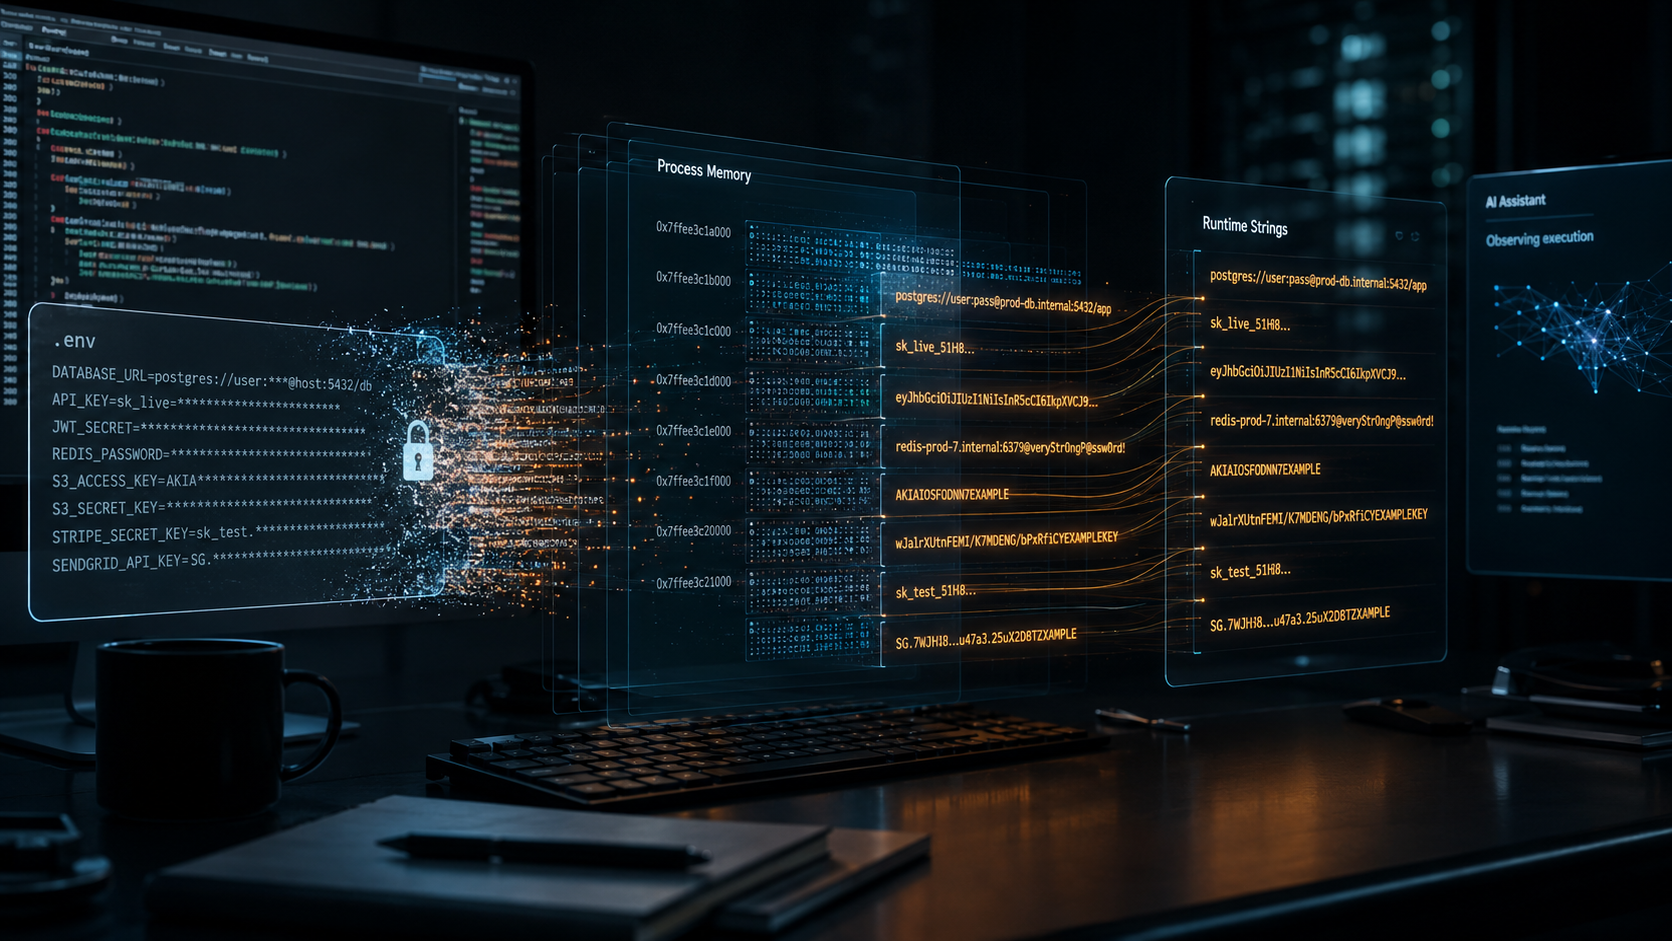
Secure secret storage is not enough if an AI agent can still read the credential at runtime. This article examines credential brokering as a way to separate service access from credential possession.

AI agents should not receive authority simply because they appear capable. Trust must be scoped, enforced by architecture, supported by evidence, and remain revocable.

Prompt injection becomes dangerous when AI agents can access tools, data, and external systems. Secure architectures must assume it will happen and limit the damage.

GitHub repositories are no longer just source control. Modern repositories act as software supply-chain entry points, making visibility, governance, SBOMs, and static analysis increasingly important security controls.

LangGraph is revolutionizing AI agent development with its graph-based structures that enhance adaptability and integration across various platforms.

AI tools don't need your .env file. Runtime access is enough. That's the shift most developers haven't caught up with yet.